SHIBA Ransomware Claims German HVAC Provider
SHIBA ransomware has claimed a data breach targeting German building services provider TEMA Haus- und Wärmetechnik. Learn about the threat group's double-extortion tactics, initial access vectors, PowerShell execution patterns, and actionable defense strategies for critical enterprise infrastructure.
Key Takeaways
- SHIBA ransomware added German HVAC provider TEMA Haus- und Wärmetechnik to its data leak site on November 1, 2026.
- The threat collective leverages double-extortion tactics, demanding ransom payments under the threat of public data disclosure.
- Initial ingress vectors frequently involve compromised remote access credentials, exposed external interfaces, or supply chain scripts.
- Defenders must monitor PowerShell web requests, enforce robust multi-factor authentication, and monitor outbound archive transfers.
Securing exposed remote access infrastructure, auditing identity directories, and evaluating perimeter boundaries represent immediate priorities for defenders after threat groups expand extortion targeting across European technical service providers. Commercial heating, ventilation, and air conditioning contractors manage sensitive architectural blueprints, operational network interconnects, and vendor access credentials. When an extortion group claims unauthorized access into such an organization, security teams must quickly examine internal telemetry to confirm whether external threat actors have leveraged legitimate credentials, unmonitored scripts, or software supply chain channels to establish persistent foothold access.
What Happened in the TEMA Haus- und Wärmetechnik Incident
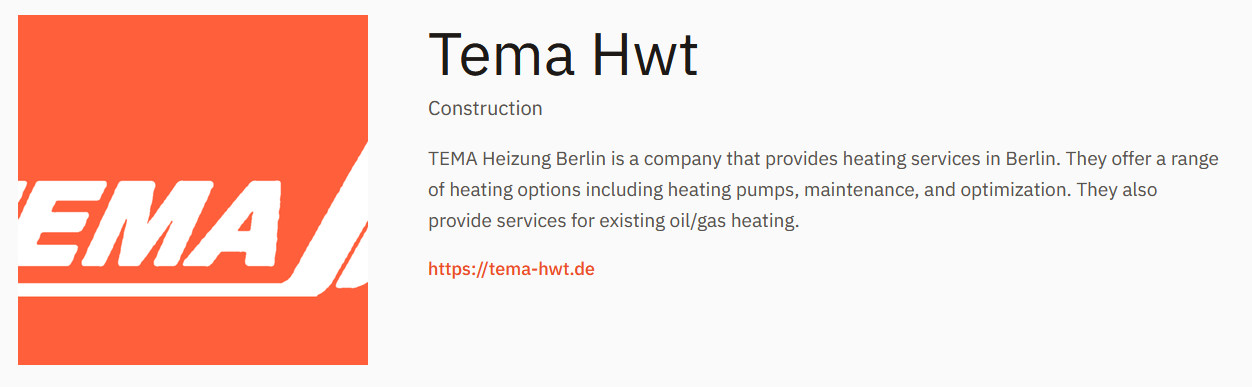
On November 1, 2026, the extortion collective known as SHIBA publicly added German building services specialist TEMA Haus- und Wärmetechnik GmbH to its Tor-hosted data leak portal. Operating from Berlin, TEMA provides specialized heating and building engineering services across Germany through the domain tema-hwt.de. The threat operators published the firm alongside claims that they had exfiltrated proprietary corporate records, internal operational documents, and confidential client data from the organization's network.
The threat group published an extortion countdown timer alongside proof indicators on their onion-routed leak platform, threatening to publicly release or broker the stolen databases if payment terms are not met. While public telemetry from government incident responders has not yet disclosed whether the intrusion included fleet-wide endpoint encryption or was limited strictly to data exfiltration, the group's pattern aligns with contemporary double-extortion practices. Incident response personnel evaluating similar intrusions typically focus on validating initial ingress paths, containing compromised administrator accounts, and inspecting staging repositories used to pack corporate archives prior to outbound transmission.
For organizations operating across industrial contracting, energy, and engineering ecosystems, this incident underlines the risk posed by secondary service providers. Threat actors increasingly focus on technical contractors that bridge internal client installations with broader commercial facilities, using any compromised access as a staging ground for wider corporate and supply chain exploitation.
How the SHIBA Ransomware Operates
Understanding the operational behavior of SHIBA requires analyzing how modern extortion syndicates combine targeted reconnaissance, multi-stage script execution, and alternative protocol exfiltration. While earlier campaigns linked to the Shiba moniker focused on developer environments through typosquatted packages, the group's current enterprise tradecraft mirrors modern human-operated ransomware gangs.
Initial Intrusion and Perimeter Exploitation
SHIBA operators typically achieve initial access through exposed remote desktop protocol endpoints, single-factor VPN gateways, or stolen corporate session tokens purchased from initial access brokers. Attackers also maintain historical capability in software supply chain vectors, having previously used rogue packages and repository squatting to drop malicious loaders into corporate development environments. Once inside, the operators prioritize fast environment reconnaissance using standard administrative utilities to minimize defensive alarms.
Execution, Living-off-the-Land, and Evasion
During the intrusion execution phase, the threat actors rely heavily on built-in Windows command interpreters. PowerShell and Windows Command Shell scripts are executed to download secondary binary stages from remote bulletproof servers, decode base64 payloads, and bypass local security policies.
Scripting Execution: PowerShell invocations utilize cmdlets such as
Invoke-WebRequest,DownloadString, or web client wrappers to pull obfuscated droppers into temporary user directories.Masquerading (T1036): Executable payloads and secondary toolsets are routinely renamed to resemble legitimate background services, standard print monitors, or Windows update binaries to evade basic process monitoring.
Credential Harvesting: Adversaries extract plaintext passwords, Kerberos tickets, and local security authority subsystem secrets to enable seamless privilege escalation across local subnets.
Exfiltration and Double-Extortion Mechanics
Prior to deploying any encryption routine, SHIBA operators stage and exfiltrate high-value intellectual property, employee records, accounting archives, and operational schematics. The data is packed into password-protected archives using command-line utilities such as 7-Zip or WinRAR, then funneled out of the environment over encrypted outbound protocols. Exfiltration channels often blend into routine administrative traffic by utilizing cloud storage application interfaces or remote staging servers. Only after confirming successful exfiltration do operators launch cryptographic routines to lock local shares, generate ransom instructions, and post the target details to their leak portal.
SHIBA Ransomware Attack Progression
- 1Initial Ingress
Exposed RDP, VPN gateways, or compromised access credentials
- 2PowerShell Execution
Living-off-the-land scripts fetch secondary droppers
- 3Defense Evasion
Masquerading payloads as benign background services
- 4Data Staging
Compressing files into password-protected archives (7-Zip/WinRAR)
- 5Double Extortion
Tor leak site listing with countdown timer & encryption
Adversary TTPs (MITRE ATT&CK Mapping)
Who Is Behind the SHIBA Threat Actor Group
The SHIBA group functions as an opportunistic cyber extortion operation tracking targets across Europe, North America, and parts of Asia. First noted in cybersecurity intelligence reporting for targeting developer ecosystems through tainted extensions, the group has evolved into a structured data extortion and crypto-ransomware operation. The actors target mid-market enterprises across manufacturing, building automation, healthcare, logistics, and technical consulting sectors.
Security researchers classify the collective as an agile, financially motivated syndicate that alternates between pure data-theft extortion and end-to-end ransomware deployment. By establishing a dedicated Tor-based leak portal, the group mirrors the operational structure of established ransomware-as-a-service enterprises. Their infrastructure relies on distributed bulletproof hosting networks, including known command-and-control hosting nodes such as 196.251.107.109, which facilitate payload hosting, external coordination, and exfiltration staging.
Unlike state-backed actors driven by espionage or destructive sabotage, SHIBA's primary objective remains financial monetization. By exploiting mid-sized contractors and service firms, the threat actors bet that operational downtime, contractual liabilities, and the risk of regulatory penalties under European data protection laws will compel victims to enter settlement negotiations.
Threat Actor Dossier: SHIBA
- Motivation
- Financial Extortion
- Targets
- Building Services & HVACManufacturingHealthcareLogisticsDeveloper Ecosystems
- TTPs
- PowerShell DownloadersProcess MasqueradingAlternative Protocol ExfiltrationDedicated Tor DLS Extortion
Enterprise Impact and Extortion Pressure
When an infrastructure and engineering provider suffers an extortion attack, the consequences extend far beyond the immediate target. The compromise of engineering files, system integration credentials, and client documentation creates systemic vulnerabilities for downstream enterprise customers who rely on those contractors for critical facility maintenance.
Organizations facing double-extortion pressure encounter several acute risks:
Operational Disruption: Containment protocols, system re-imaging, and network segmentation abruptly stall day-to-day service delivery, administrative operations, and client project timelines.
Regulatory and Compliance Exposure: Under stringent data protection regulations such as the GDPR, organizations losing control over customer, personnel, or partner data face mandatory 72-hour reporting windows and potential statutory penalties.
Downstream Supply Chain Infiltration: Client architectural schematics, building management network diagrams, and stored credentials can be weaponized by threat actors to map or compromise client facilities.
Reputational Damage: Publication on public leak sites exposes operational compromises to partners, competitors, and industry regulators, undermining commercial credibility.
Comprehensive risk reduction requires rigorous validation of external perimeters and identity stores. Conducting regular penetration testing enables enterprises to identify exploitable configuration weaknesses, unpatched edge devices, and lateral movement paths before malicious operators discover them. Additionally, maintaining continuous attack surface management ensures internet-facing endpoints and unmanaged cloud services do not serve as unmonitored entry gates for ransomware groups.
Free exposure check
Dark Web Scanner
check dark web mentions, compromised account indicators, malware log signals, public breach exposure, and recent underground market activity for your domain.
Downstream Contractor Compromise Blast Radius
- Client Architectural Schematicshigh
- Facility Access Credentialshigh
- GDPR Compliance Liabilitiesmedium
- Operational Service Outageshigh
- Public Leak Site Disclosuresmedium
Proactive Detection and Containment Strategies
Defenders must deploy proactive detection logic and disciplined containment procedures to detect SHIBA indicators and mitigate ransomware staging before data exfiltration occurs.
Endpoint and Telemetry Hunting Logic
Security teams should implement behavioral rules across endpoint detection and response platforms to identify unauthorized PowerShell execution, encoded web downloads, and abnormal script interpreter activity. The following detection logic identifies suspicious command-line patterns commonly associated with secondary stage ransomware fetchers:
title: Suspicious PowerShell Payload Retrieval (Shiba-Style Downloader)
logsource:
    category: process_creation
    product: windows
detection:
    selection_cmd:
        Image|endswith:
            - '\powershell.exe'
            - '\pwsh.exe'
        CommandLine|contains:
            - 'DownloadString'
            - 'DownloadFile'
            - 'Invoke-WebRequest'
            - 'iwr'
    condition: selection_cmd
level: high
In addition to process creation monitoring, security analysts should inspect Windows Event logs for PowerShell Script Block Logging (Event ID 4104) and Module Logging (Event ID 4103). These logs expose de-obfuscated script commands, revealing staging destinations and memory-injected execution strings.
Network Traffic and Infrastructure Auditing
Defenders should audit border firewalls, proxy appliances, and DNS resolvers for unusual egress volumes and communication with suspect autonomous systems. Key network hunting actions include:
Blocking outbound network connectivity toward confirmed threat infrastructure, including IP address
196.251.107.109.Flagging sudden outbound volume spikes to untrusted external IP addresses, particularly when involving large compressed archive extensions such as
.7z,.zip, or.rar.Restricting and monitoring outbound SSH, RDP, and custom TLS connections initiated by non-standard system processes.
Immediate Containment and Hardening Actions
If suspicious activity or credential anomalies are detected, organizations must immediately initiate structured containment protocols:
Isolate Suspect Endpoints: Disconnect affected workstations and servers from the local area network and wireless segments to interrupt active command-and-control communication and stop lateral movement.
Revoke and Rotate Identity Credentials: Force enterprise-wide password resets for all corporate, administrative, and service accounts. Terminate active Kerberos and web application sessions immediately.
Enforce Phishing-Resistant MFA: Require multi-factor authentication across all virtual private networks, remote desktop gateways, and software-as-a-service portals, restricting access to approved hardware tokens or authenticator apps.
Preserve Forensic Artifacts: Collect non-volatile disk images, volatile memory snapshots, and perimeter firewall logs before rebooting or re-imaging compromised systems to support definitive root-cause analysis.
Harden Software Supply Chains: Restrict third-party script execution, enforce software restriction policies, and permit only verified code repositories within enterprise developer and administrative environments.
Threat Group Infrastructure & Target Identifiers
- ip196.251.107.109SHIBA C2 and staging infrastructureip196.251.107.109SHIBA C2 and staging infrastructure
- domaintema-hwt.deTarget organization web domaindomaintema-hwt.deTarget organization web domain
Incident Containment and Hardening Actions
- Block outbound traffic to C2 hosting node 196.251.107.109Network perimeter firewall and proxy rules
- Isolate compromised hosts and terminate active sessionsSever LAN/WLAN connections to contain lateral spread
- Force enterprise credential rotationReset passwords for administrative and domain accounts
- Enforce phishing-resistant MFA across perimeter portalsRDP, VPN endpoints, and cloud services
- Enable PowerShell Script Block Logging (Event ID 4104)Capture de-obfuscated secondary-stage payloads
- Preserve volatile memory and event log artifactsCollect evidence prior to system re-imaging
How to Defend Against Similar Threats
- Block outbound network traffic to known SHIBA infrastructure, including C2 IP address 196.251.107.109.
- Implement process creation rules targeting PowerShell downloaders using Invoke-WebRequest and DownloadString cmdlets.
- Audit all remote access pathways, including VPNs and RDP services, enforcing phishing-resistant multi-factor authentication.
- Review internal user accounts and conduct lateral movement assessments across industrial and building automation subnets.
Threat Intel FAQ
What is SHIBA ransomware?
How did SHIBA ransomware compromise TEMA Haus- und Wärmetechnik?
What immediate steps should defenders take to detect SHIBA activity?
Could a similar threat affect your organization?
If your team may be exposed to a similar threat, FemtoSec can help validate blast radius, prioritize remediation, and connect the issue to a practical security program.
Related Threats
October 23, 2026
Kazu Ransomware Targets Insurance Sector in 366 GB Breach
Kazu ransomware operators have listed South African insurer Rand Mutual Assurance on their dark web leak portal, claiming 366 GB of exfiltrated corporate records. This intelligence brief examines Kazu's attack tradecraft, LockBit lineage, operational impact, and concrete detection rules.
October 16, 2026
Play Ransomware Targets The Innovation Group
Play ransomware operators have targeted United States management consulting firm The Innovation Group, publishing claims on their dark web leak site with a four to five day deadline to release stolen corporate data.
October 5, 2026
Spirals Ransomware Hits Seven Seas Group in GCC
Spirals ransomware has claimed the compromise of GCC-based maritime services provider Seven Seas Group, demanding ransom under a strict data leak countdown. This incident underscores critical risks across regional logistics and transportation infrastructure.