Anonymous Mobile RAT v6 Analysis
Underground threat actors have announced the release of Anonymous Mobile RAT v6, an advanced Android Remote Access Trojan designed to capture credentials, record screens, and abuse accessibility settings, creating severe risks for enterprise mobile security.
Key Takeaways
- Anonymous Mobile RAT v6 leverages Accessibility Services abuse to silently elevate system privileges without user authorization.
- The malware circumvents background management and battery-saving features native to specialized mobile hardware configurations.
- It bypasses Android secure screen flags by programmatically reading UI layouts using a screen-reading parser.
- Interception of incoming SMS messages nullifies standard SMS-based multi-factor authentication safety measures.
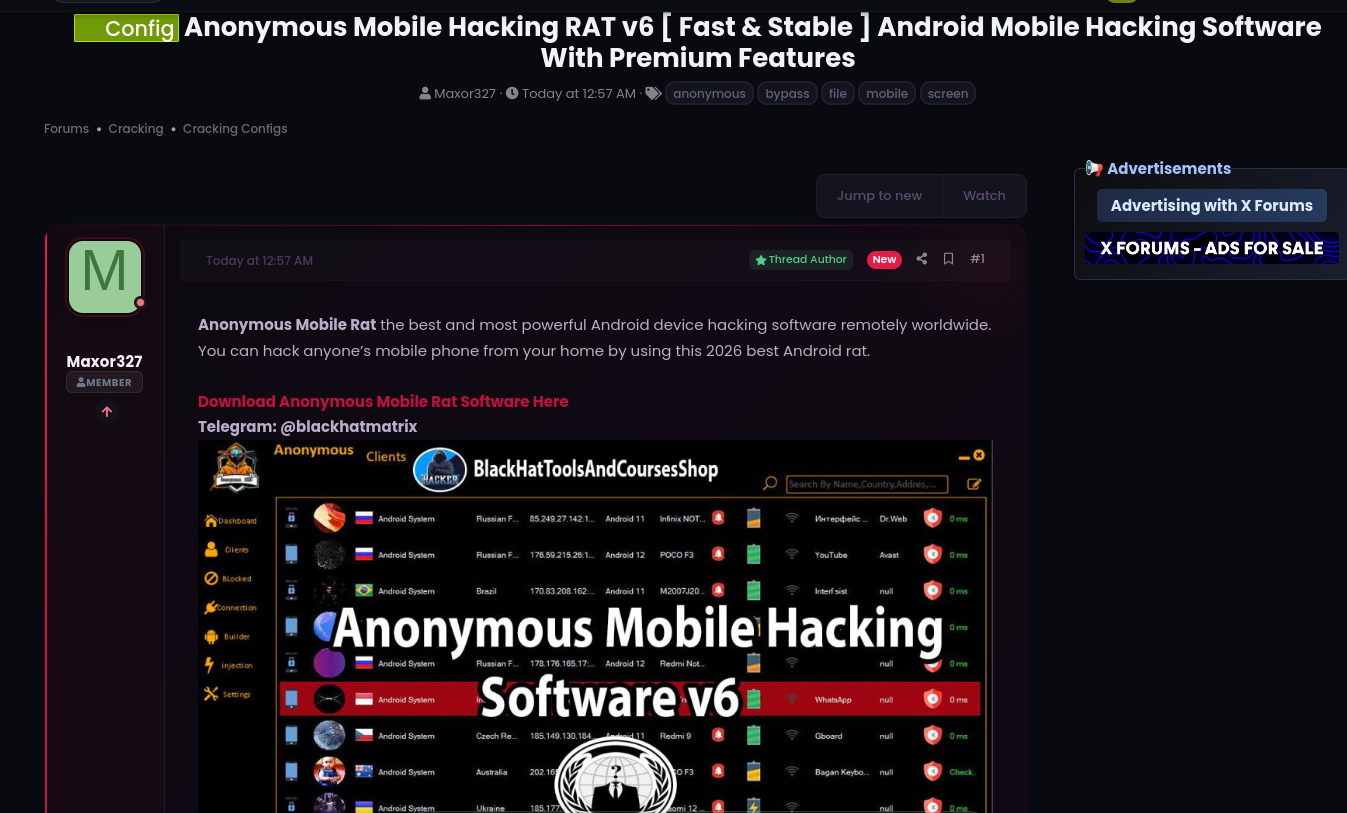
Threat actors on dark web hacking forums have announced the release of Anonymous Mobile RAT v6, a highly sophisticated, commercially distributed Android Remote Access Trojan designed to hijack mobile devices. The release, which surfaced on specialized cybercrime marketplaces such as xforums.st, marks a significant upgrade in the capabilities available to mobile-focused threat actors. This premium mobile malware suite is engineered to facilitate extensive real-time monitoring, absolute interactive remote control, and sensitive data harvesting, primarily targeting mobile banking applications and cryptocurrency wallets. By delivering an all-in-one surveillance engine, the developers of this remote access trojan (RAT) present a direct threat to corporate mobile fleets and personal privacy alike. The threat landscape in the GCC region has seen a sharp increase in mobile-centric cyber threats, making the arrival of version 6 a critical concern for regional enterprises. Security operations teams must recognize that modern mobile operating systems are no longer safe havens, as advanced threat actors continuously evolve their toolkits to bypass standard defense mechanisms. For organizations striving to maintain a resilient posture, understanding the deployment methods and technical mechanics of this threat is essential. If you suspect that your corporate assets or credentials have been exposed on these cybercrime forums, performing a proactive check using FemtoSec's Dark Web Scanner can provide immediate visibility into leaked data.
AMRAT v6 Attack & Deployment Chain
- 1Delivery & Binding
Legitimate APK is injected with the AMRAT payload using the built-in Advance Binder.
- 2Privilege Escalation
Malware abuses Android Accessibility Services to auto-grant runtime system permissions.
- 3Defense Evasion
Google Play Protect is disabled; persistence is locked using Device Administrator privileges.
- 4Interactive C2
Attackers launch VNC sessions, bypass secure windows via screen readers, and harvest data.
Deep Technical Analysis of the AMRAT v6 Attack Chain
Understanding the capabilities of Anonymous Mobile RAT v6 requires looking into its structured, multi-phase attack chain. This malicious toolset does not rely on zero-day operating system exploits; instead, it aggressively abuses standard, high-privilege Android features and system configurations.
Phase 1: Delivery and Initial Access via Advanced Binding
The primary delivery mechanism for this RAT relies on social engineering, spear-phishing campaigns, and malicious links distributed via platforms like Telegram and Discord. Threat actors utilize the malware's built-in Advance Binder utility to merge the malicious payload into legitimate Android Package (APK) files. These targeted applications typically mimic widely used utilities, messaging apps, or system updates. When the victim installs and runs the compromised application, the original utility operates normally in the foreground to prevent suspicion, while the RAT silently launches its initial setup in the background.
Phase 2: Privilege Escalation and Defense Evasion
Once active, the malware initiates an aggressive sequence to secure administrative and system privileges:
Abuse of Accessibility Services: The application repeatedly prompts the victim to enable Android Accessibility Services. Once this permission is granted, the RAT gains programmatic control over the device UI. It uses this control to automatically click through subsequent system dialogs, silently granting itself high-risk permissions such as SMS access, call reading, and directory access without further user interaction.
Play Protect and Security Evasion: The malware attempts to disable Google Play Protect and suppresses security notifications from local mobile threat defense tools, ensuring its background operations remain undetected.
Bypassing Chinese OS Customizations: Modern Chinese smartphone operating systems, including Xiaomi's MIUI/HyperOS and Huawei's EMUI, incorporate strict background process managers that shut down inactive services. Anonymous Mobile RAT v6 features dedicated code blocks specifically engineered to bypass these vendor optimizations, maintaining a persistent background connection.
Anti-kill and Anti-delete Routines: By prompting the user to grant Device Administrator permissions, the malware locks its presence on the device. It alters the standard application uninstallation path, preventing the user or automated cleanup utilities from removing the package.
Phase 3: Interactive Remote Control and Financial Hijacking
The core of the Trojan's operational utility is its real-time command-and-control (C2) capability, allowing attackers to manipulate the device remotely:
Silent Interactive VNC Screen Control: Attackers can establish a low-latency, interactive Virtual Network Computing (VNC) session. This permits the attacker to view the live mobile screen and send remote touch inputs, effectively taking physical control of the device from afar.
Bypassing FLAG_SECURE via Screen Reader Tech: Many high-security apps, such as corporate banking or cryptocurrency wallets, activate the system secure flag to prevent screenshots and screen capture. To circumvent this, AMRAT v6 integrates a custom screen-reading layout parser. It reads the raw UI text from the active screen buffers, rendering the textual layout back to the attacker as text, bypassing the black-screen security measure.
HTML Overlay Injection: The RAT monitors the device's foreground application. When a targeted banking, financial, or corporate application is opened, the malware injects a custom HTML overlay. This overlay acts as a credential harvesting screen, harvesting corporate logins and multi-factor authentication codes.
Active Surveillance: The software supports ambient microphone recording, front-and-back camera access, real-time GPS coordinates tracking, keylogging of all onscreen keystrokes, and active call/SMS interception.
AMRAT v6 Target Areas & Blast Radius
- Mobile Banking Credentialshigh
- Cryptocurrency Walletshigh
- SMS Verification Codes (OTPs)high
- Corporate App Logins & Emailshigh
- Ambient Environment Surveillancemedium
Mapping Threat Behaviors to the MITRE ATT&CK Framework
The tactical operations of Anonymous Mobile RAT v6 line up with several known categories within the MITRE ATT&CK Matrix for Mobile:
Initial Access: T1476 (Deliver Malicious App via Other Means) - Utilizes external binder scripts to package payloads inside benign APK files.
Execution: T1204 (User Execution) - Relies on initial social engineering to convince the victim to execute the installer.
Persistence: T1624.001 (Event-Triggered Execution: Broadcast Receivers) - Listens for system boot actions to restart C2 communication loops.
Privilege Escalation: T1453 (Abuse Accessibility Features) - Automates user authorization clicks.
Defense Evasion: T1628.001 (Suppress Application Icon) - Disables the launcher icon to avoid visual detection by the end-user.
Credential Access: T1417.001 (Input Capture: Keylogging) and T1417.002 (Input Capture: GUI Input Capture) - Records direct on-screen keyboard strokes and deploys phishing overlays.
Collection: T1513 (Screen Capture) and T1429 (Audio Capture) - Captures remote screen data and microphone streams.
AMRAT v6 Tactical Mapping to MITRE ATT&CK
Enterprise Exposure and Strategic Mitigation
For enterprises across the GCC, the widespread availability of tools like Anonymous Mobile RAT v6 significantly elevates the threat of corporate network intrusion. When an employee's personal or corporate mobile device is compromised, attackers gain immediate access to enterprise email accounts, VPN configurations, and critical corporate credentials. Furthermore, because the malware intercepts incoming SMS messages, traditional SMS-based multi-factor authentication (MFA) is rendered entirely ineffective. To mitigate this operational risk, organizations must move beyond traditional mobile device management (MDM) policies and adopt a proactive offensive posture. Implementing comprehensive security controls, including continuous monitoring and proactive testing, is essential. Organizations should regularly simulate real-world mobile threats and app-binding scenarios. Discovering exposed assets across the digital perimeter can be achieved by utilizing FemtoSec's Attack Surface Management program to ensure rogue endpoints or rogue distribution paths are identified early. Additionally, subscribing to Dark Web Monitoring keeps organizations informed when credentials belonging to their domain are listed on underground forums like fullcrypters.net or associated with active Telegram operations like @Haxk_zone.
AMRAT v6 Known Indicators of Compromise
- domainfullcrypters.netDistribution & actor forum domaindomainfullcrypters.netDistribution & actor forum domain
- domaint.me/Haxk_zoneActor/Seller Telegram channeldomaint.me/Haxk_zoneActor/Seller Telegram channel
- urlhxxps://mega.nz/file/ZKMBVJZA#NxRWc5Q0ynxMyl-6EMSqEoQfUG8nB2ExyYoqTs5003ILeaked build package URLurlhxxps://mega.nz/file/ZKMBVJZA#NxRWc5Q0ynxMyl-6EMSqEoQfUG8nB2ExyYoqTs5003ILeaked build package URL
Detection Logic, Verification, and Emergency Containment
Security operations center (SOC) analysts and mobile administrators can establish specific monitoring parameters to identify and isolate active infections.
1. Concrete Detection Logic
On-Device Manifest Audits: Scan active applications for the simultaneous presence of high-risk permissions. Specifically, any third-party app requesting
android.permission.BIND_ACCESSIBILITY_SERVICEin combination withandroid.permission.SYSTEM_ALERT_WINDOW(Draw Over Other Apps) must be treated as critical risk.Network Telemetry: Audit mobile gateway logs and enterprise Wi-Fi connections for outbound socket handshakes over non-standard ports (such as 8080, 7777, or 9090) directed toward dynamic DNS providers (such as No-IP or Ngrok) or unverified virtual private server (VPS) subnets.
Static APK Analysis: Ensure that sideloaded applications are routinely disassembled and scanned for references to VNC layout rendering engines or accessibility node parser APIs.
2. Verification Procedures
To verify an infection on a suspected Android device:
Go to Settings and navigate to Apps > Special App Access.
Select Accessibility Services and review the list of apps granted active access. Any unauthorized utility should be flagged.
Review Device Admin Apps to confirm that no unknown applications have assumed control of screen-lock configurations or remote wipe capabilities.
Utilize a dedicated Mobile Threat Defense (MTD) scanner to analyze sideloaded software for signature-based anomalies.
3. Containment and Remediation Measures
If an infection is confirmed:
Network Isolation: Put the mobile device in Airplane Mode immediately or disconnect it from cellular and Wi-Fi networks to sever the active connection with the command-and-control server.
Revoke Permissions: Manually navigate to system settings, strip the malicious application of Device Administrator access, and turn off its Accessibility permissions.
Safe Mode Uninstall: Uninstall the application. If the application uses anti-delete loops to block access to the uninstall screen, restart the Android device in Safe Mode to execute the removal.
Complete System Wipe: Because the RAT intercepts sensitive database structures and keys, a full factory reset of the mobile device is highly recommended to guarantee complete eradication.
Credential and MFA Revocation: Immediately reset all corporate and personal passwords accessed on the device, terminate active web sessions, and migrate security accounts to hardware token-based multi-factor authentication rather than SMS-based OTPs.
Enterprise Mobile Incident Containment Steps
- Network IsolationActivate Airplane Mode immediately on infected endpoints to sever C2 socket connections.
- Revoke Active PrivilegesManually strip Device Administrator status and disable active Accessibility permissions.
- Safe Mode UninstallationBoot device in Safe Mode to bypass anti-delete loops and cleanly uninstall the malicious utility.
- Complete System WipeExecute a hardware-level factory reset to wipe all residual credentials and spyware hooks.
- Rotate Corporate LoginsForce credential rotation for all business systems accessed by the user and revoke existing active sessions.
How to Defend Against Similar Threats
- Deploy unified endpoint management controls to strictly prevent unauthorized sideloading of third-party applications.
- Enforce hardware-token or authenticator-app-based MFA across all corporate portals to neutralize SMS interception risks.
- Perform continuous attack surface mapping and check for leaked domain indicators using automated scanner tools.
- Instruct security teams to regularly audit accessibility permission states on corporate-owned Android mobile fleets.
Threat Intel FAQ
How does Anonymous Mobile RAT v6 bypass on-device security controls?
Why is SMS-based multi-factor authentication ineffective against this RAT?
Could a similar threat affect your organization?
If your team may be exposed to a similar threat, FemtoSec can help validate blast radius, prioritize remediation, and connect the issue to a practical security program.
Related Threats
July 25, 2026
BTMOB RAT v4.6 Mobile Malware Threat Analysis
Defenders prioritizing mobile endpoint integrity must immediately audit Android Accessibility Service authorizations to counter BTMOB RAT v4.6. This technical analysis explores the malware's delivery vectors, capabilities like 2FA bypass, and step-by-step containment protocols.
October 7, 2026
AbkoRAT License Sale Fuels Remote Surveillance Threat
Underground forums have observed threat actors commercializing AbkoRAT, a commercial Remote Access Trojan engineered for stealthy surveillance, multimedia interception, credential harvesting, and arbitrary command execution across compromised enterprise hosts.
September 18, 2026
Hermes Stealer Emerges with HVNC and Token Theft
A new malware-as-a-service offering named Hermes has surfaced on underground forums, bundling hidden virtual desktop control, browser credential harvesting, crypto wallet theft, and remote command execution.