Play Ransomware Targets The Innovation Group
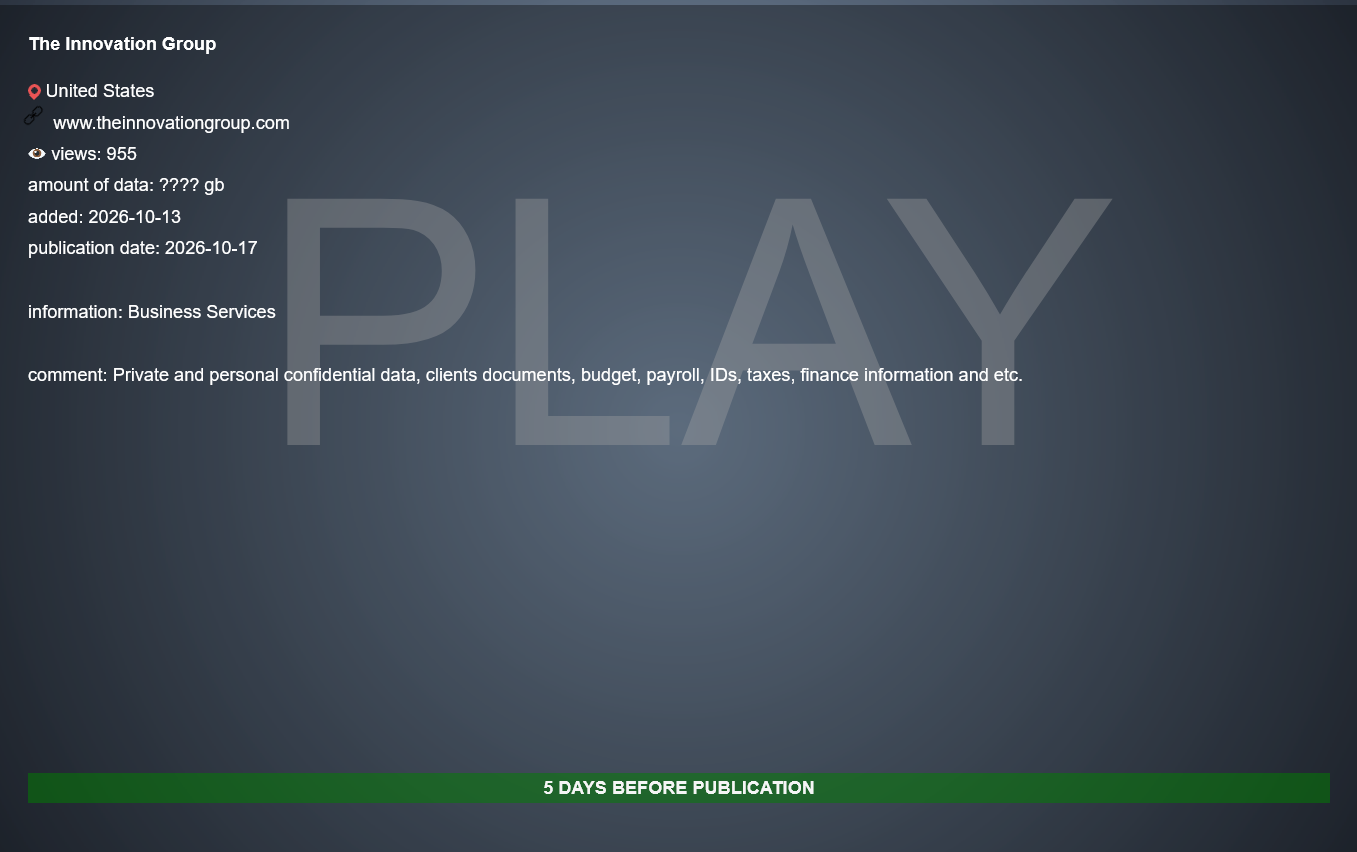
Play ransomware operators have targeted United States management consulting firm The Innovation Group, publishing claims on their dark web leak site with a four to five day deadline to release stolen corporate data.
Key Takeaways
- Play ransomware added US management consulting firm The Innovation Group to its Tor leak site, issuing a 4 to 5 day publishing deadline.
- The threat group utilizes double extortion, stealing sensitive corporate files before triggering system encryption.
- Play operators frequently disable endpoint defenses using custom tools and target both Windows environments and VMware ESXi hypervisors.
- Mitigation requires restricting hypervisor access, monitoring for shadow copy deletion, and validating immutable backup systems.
Play ransomware operators added United States management consulting firm The Innovation Group to their dark web leak repository, threatening to leak exfiltrated corporate records unless extortion demands are satisfied within four to five days. The threat actors claim to have obtained sensitive organizational data from internal corporate networks, placing intense operational and regulatory pressure on the advisory practice.
Advisory Sector Blast Radius
- Gaming & leisure clientshigh
- Proprietary economic modelshigh
- Internal corporate networkhigh
- Feasibility & advisory filesmedium
What Happened in the Incident
On October 13, 2026, the Play extortion syndicate posted an entry targeting The Innovation Group on their Tor-hosted double-extortion portal. According to the listing, the group gained access to the firm's systems, staged corporate data, and initiated an extortion cycle with a short disclosure deadline. The threat actors set a timer between four and five days, warning that all stolen archives will be published publicly if negotiations do not commence.
The Innovation Group provides specialized economic advisory, financial modeling, management consulting, and feasibility studies to global entertainment, gaming, and leisure enterprises. The exfiltration of advisory files presents substantial third-party data exposure risks for client portfolios. While internal forensic assessments remain ongoing and victim-side post-mortems have not been publicly disclosed, the operational pattern matches the structured double-extortion playbooks executed by the syndicate across professional services firms.
Organizations experiencing external exposure threats can conduct proactive assessments across corporate infrastructure through comprehensive penetration testing to validate perimeter controls before adversaries execute data staging operations.
Play Ransomware Attack Sequence
- 1Initial Access
Exposed RDP, VPN credentials, or edge flaws
- 2Defense Evasion
Disable Defender via PowerShell; GMER / PowerTool
- 3Discovery
AdFind, BloodHound, and WinPEAS domain mapping
- 4Credential Dumping
Mimikatz LSASS harvesting & SAM dumping
- 5Exfiltration
WinRAR / 7-Zip staging via WinSCP and rclone
- 6Impact
.play encryption & vssadmin shadow deletion
How the Ransomware Operates and Executes
Play ransomware operates using an organized multi-phase attack chain focused on remote compromise, credential harvesting, defense evasion, high-speed data exfiltration, and hypervisor-level disruption. The gang relies on both custom-compiled encryptor binaries and dual-use living-off-the-land tools to evade automated detection platforms.
Attack Chain and Initial Access Vectors
The operational attack chain observed across Play ransomware intrusions typically follows six distinct structural phases:
Initial Perimeter Penetration: Operators gain initial access by targeting exposed Remote Desktop Protocol (RDP) services, abusing stolen VPN credentials, or exploiting public-facing network appliances and remote monitoring systems.
Defense Evasion and Security Disablement: Once inside a target machine, operators execute batch scripts and PowerShell commands to terminate security agents. They frequently run commands such as
Set-MpPreference -DisableRealtimeMonitoring $trueand use low-level process termination utilities like GMER or PowerTool to blind endpoint security tools.Internal Discovery and Active Directory Mapping: The group deploys automated reconnaissance utilities, including
AdFind,BloodHound, andWinPEAS, to identify domain trust relationships, user groups, and privilege escalation pathways.Credential Dumping and Lateral Progression: Threat actors harvest credentials from LSASS memory using Mimikatz and dump SAM registry hives. Lateral movement is executed across internal subnets using PsExec, Cobalt Strike beacons, Windows Remote Management (WinRM), and SystemBC proxy tunnels.
Archive Staging and Data Exfiltration: Sensitive files, corporate documents, and financial records are compressed into password-protected archives using command-line WinRAR or 7-Zip. These staging archives are exfiltrated over encrypted channels via WinSCP, rclone, or Plink reverse port-forwarding sessions before encryption starts.
Cryptographic Deployment and Shadow Copy Deletion: The ransomware binary executes across domain controllers, shared drives, and VMware ESXi environments, appending the
.playfile extension. System recovery is blocked by executingvssadmin delete shadows /all /quietand clearing Windows event logs withwevtutil cl system.
MITRE ATT&CK Behavioral Mapping
Play operations consistently demonstrate mapped behaviors across the MITRE ATT&CK framework:
Initial Access (T1190 / T1078): Exploit Public-Facing Application and Valid Accounts through perimeter gateways.
Execution (T1059.001 / T1569.002): PowerShell script execution and Service Execution via PsExec for payload delivery.
Defense Evasion (T1562.001 / T1070.001): Impair Defenses by disabling antivirus controls and Indicator Removal via event log wiping.
Credential Access (T1003.001): OS Credential Dumping targeting LSASS memory.
Lateral Movement (T1021.001 / T1021.002): Interactive RDP usage and SMB Windows Admin Shares.
Impact (T1486 / T1490): Data Encrypted for Impact using the PlayCrypt binary and Inhibit System Recovery via Volume Shadow Copy deletion.
Who Is Behind the Play Threat Actor Group
Play ransomware, also tracked by intelligence analysts as PlayCrypt and Balloonfly, first surfaced in June 2022. The group originated as a closed, highly disciplined extortion collective before developing relationships with specialized initial access brokers. Unlike many contemporary Ransomware-as-a-Service operations that provide victim negotiation portals directly on Tor hidden services, Play operators frequently mandate that victims communicate via single-use, privacy-focused email services such as GMX or Web.de using unique identification keys left in ransom notes.
The syndicate has historically avoided geographic boundaries, hitting public sector bodies, manufacturing entities, and professional services groups across the Americas, Europe, and international commercial hubs. In addition to standard Windows server and desktop payloads, Play maintains dedicated Linux and VMware ESXi encryptors designed to shut down enterprise virtual machines and encrypt underlying .vmdk files directly from hypervisor command shells.
Threat Actor Profile: Play Ransomware
- Motivation
- Financial extortion
- Targets
- Consulting & advisory servicesHospitality, gaming & entertainmentManufacturingPublic sector
- TTPs
- Double extortion with public leak countdownsGMX and Web.de webmail ransom negotiation channelsWindows & VMware ESXi hypervisor encryptionPowerShell & batch script defense evasion
Enterprise Impact and Extortion Pressure
Targeting a strategic consulting group highlights an evolving focus on high-value business intermediaries. When consulting networks are breached, the impact extends beyond direct operational interruption to include downstream client exposure. Advisory firms harbor proprietary economic models, merger evaluations, strategic client roadmaps, and detailed financial audits.
The threat actors utilize the strict four to five day publication deadline to impose severe extortion pressure on executive leadership. Double-extortion techniques remove the safety net provided by standard offline backups; even if an enterprise restores its databases seamlessly, the threat of public document exposure creates intense regulatory scrutiny under data privacy statutes, contractual liability from corporate clients, and reputational erosion.
To evaluate whether leaked domain accounts or corporate credentials have surfaced in underground channels following perimeter compromises, teams can check exposed indicators through defensive audits. If the domain already looks exposed, use Dark Web Scanner before requesting a full report.
Play Ransomware Defense-in-Depth
- L1Perimeter DefenseAudit exposed RDP and administrative interfacesEnforce MFA across VPN concentrators and external accessPatch edge appliances and remote monitoring software
- L2Endpoint & IdentityAlert on PowerShell commands disabling Windows DefenderMonitor LSASS access for Mimikatz credential dumpingRevoke Kerberos tickets and reset privileged AD credentials
- L3Hypervisor IsolationRestrict ESXi management access to dedicated VLANsDisable ESXi SSH services across hypervisorsAudit ESXi shell authentication logs for anomalous access
- L4Resilience & RecoveryVerify backup repositories are air-gapped and immutableDetect shadow copy deletion via vssadmin and wmicAlert on Windows Security Event ID 1102 log clearing
Detection and Containment Strategies
Defending against Play ransomware intrusions requires synchronized endpoint detection rules, Active Directory hardening, and isolated containment workflows.
Endpoint and SIEM Detection Logic
Security operations centers should deploy specialized detection rules targeting the characteristic pre-encryption behaviors of Play operators:
Shadow Copy Destruction: Monitor Windows Event ID 4688 (Process Creation) and Sysmon Event ID 1 for command-line arguments matching
vssadmin* delete* shadows*orwmic* shadowcopy* delete*.Security Log Clearance: Trigger critical alerts on Security Event ID 1102 (The audit log was cleared) and process creation events invoking
wevtutil* cl*.Antivirus Disablement: Alert on PowerShell Event ID 4104 (Script Block Logging) capturing attempts to execute
Set-MpPreference -DisableRealtimeMonitoring $trueor manipulation of Windows Defender service registries.Rapid Mass Modification: Implement EDR behavioral tripwires for abnormal burst write actions creating files with the
.playextension alongside drop events forReadMe.txtorPLAY_Readme.txtnotes.
Immediate Containment and Hardening Guidance
When defending enterprise infrastructure against Play deployment, teams should execute immediate containment and hardening steps:
Isolate Hypervisors and Storage Arrays: Restrict management network access to VMware ESXi clusters, disable ESXi SSH services unless actively required for maintenance, and enforce multi-factor authentication across all hypervisor consoles.
Enforce Attack Surface Visibility: Identify and eliminate exposed administrative interfaces, insecure VPN concentrators, and open RDP ports by conducting continuous attack surface management assessments across all perimeter IP ranges.
Revoke Stale Identity Sessions: Force global password resets for privileged Active Directory accounts, revoke active Kerberos tickets, and enforce hardware-backed multi-factor authentication across external entry points.
Verify Backup Immutability: Ensure enterprise backup repositories are logically isolated, air-gapped, and immutable to prevent destructive deletion during the adversary's lateral movement phase.
How to Defend Against Similar Threats
- Implement SIEM alerts targeting vssadmin shadow copy deletion and wevtutil event log clearing commands.
- Audit external attack surfaces to identify and disable unauthenticated remote access portals and exposed RDP ports.
- Restrict VMware ESXi SSH and management console access to dedicated, multi-factor-authenticated management VLANs.
- Enforce phishing-resistant multi-factor authentication across all VPN gateways, remote tools, and administrative accounts.
Threat Intel FAQ
What is Play ransomware and how does it execute double extortion?
What assets are threatened in the incident involving The Innovation Group?
How can defenders detect a Play ransomware attack before encryption occurs?
Could a similar threat affect your organization?
If your team may be exposed to a similar threat, FemtoSec can help validate blast radius, prioritize remediation, and connect the issue to a practical security program.
Related Threats
October 5, 2026
Panzer Ransomware Targets Healthcare with 33GB Exfiltration
Panzer ransomware has targeted UK healthcare provider SMCare, exfiltrating 33GB of sensitive organizational data. The double-extortion campaign leverages cross-platform payloads capable of targeting Windows and VMware ESXi environments, enforcing strict countdown timers on dedicated Tor leak sites.
September 9, 2026
Vexy Ransomware Targets Retailer in 24GB Data Leak
The Vexy ransomware group has published an extortion listing targeting Argentinian retailer Librería Santa Fe, claiming 24.2 GB of exfiltrated data with a 20-day publication ultimatum. Explore technical analysis, attack chains, and defensive containment strategies.
October 5, 2026
Spirals Ransomware Hits Seven Seas Group in GCC
Spirals ransomware has claimed the compromise of GCC-based maritime services provider Seven Seas Group, demanding ransom under a strict data leak countdown. This incident underscores critical risks across regional logistics and transportation infrastructure.