Panzer Ransomware Targets Healthcare with 33GB Exfiltration
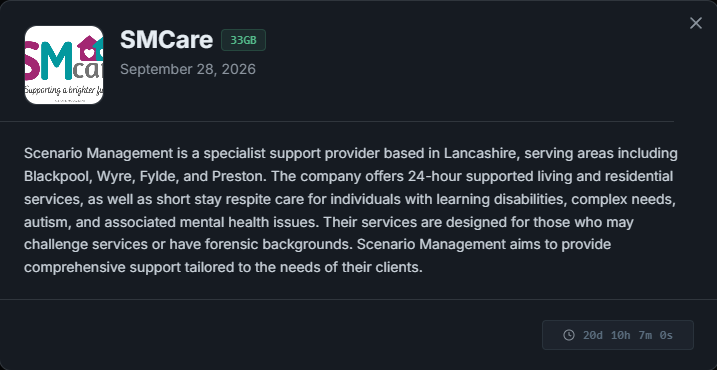
Panzer ransomware has targeted UK healthcare provider SMCare, exfiltrating 33GB of sensitive organizational data. The double-extortion campaign leverages cross-platform payloads capable of targeting Windows and VMware ESXi environments, enforcing strict countdown timers on dedicated Tor leak sites.
Key Takeaways
- Panzer ransomware listed UK healthcare provider SMCare after claiming the theft of 33GB of sensitive organizational data.
- The group utilizes a double-extortion model supported by cross-platform encryptors targeting Windows, Linux, FreeBSD, and VMware ESXi hypervisors.
- Affiliates leverage automated countdown timers on Tor leak sites to enforce extortion pressure on targeted enterprises.
- Hypervisor isolation, immutable air-gapped backups, and aggressive credential monitoring are critical to mitigating Panzer deployments.
Panzer ransomware operators have published UK healthcare and supported living provider SMCare on their dedicated Tor leak site, claiming the theft of 33GB of sensitive data and establishing a 20 to 21 day payment window before public release. The incident highlights the growing operational cadence of the Panzer syndicate, an emerging Ransomware-as-a-Service group targeting critical operational infrastructure, healthcare services, and multi-platform enterprise environments.
Panzer SMCare Incident Metrics
What Happened in the SMCare Panzer Ransomware Incident
The security breach surfaced when Panzer operators added smcare.co.uk to their Tor-based extortion portal. According to the syndicate, the exfiltrated 33GB archive contains internal organizational files and proprietary records. The threat actors have accompanied the disclosure with an automated countdown timer, warning that failure to negotiate will result in the complete release of the stolen repository.
Healthcare and social care service providers represent high-value targets for extortion groups due to the severe operational and regulatory implications of downtime and confidential record exposure. While specific primary access tokens or vulnerability vectors for this direct intrusion remain under active investigation, threat intelligence indicates Panzer affiliates systematically leverage exposed external endpoints, compromised remote access credentials, and unpatched hypervisor services to secure footholds within target networks.
Panzer Multi-Platform Exploitation Sequence
- 1Initial Access
Edge appliance vulnerabilities & brute-force RDP/SSH
- 2Discovery & Evasion
LSASS credential dumping & shadow copy deletion
- 3ESXi VM Termination
Execute vim-cmd to power off guest VMs
- 4Data Exfiltration
Stage records & exfiltrate via Rclone/SFTP
- 5Multi-OS Encryption
Encrypt .vmdk images & initiate extortion countdown
How the Ransomware Operates and Executes Across Multi-Platform Assets
Panzer operates on a multi-platform framework engineered to disrupt heterogenous enterprise networks. The ransomware payload features tailored binaries compiled for Windows, Linux, FreeBSD, and VMware ESXi hypervisors. This design enables adversaries to dismantle virtualization clusters and lock critical virtual machine disk images directly at the hypervisor layer.
1. Initial Access and Perimeter Infiltration
Affiliates operating under the Panzer banner frequently initiate intrusions through several distinct vectors mapped to MITRE ATT&CK techniques:
Exploitation of Edge Appliances (T1190): Targeting known vulnerabilities across public-facing firewall interfaces, SSL VPN concentrators, and gateway solutions.
Credential Spraying and Brute Force (T1110 / T1078): Systematically testing breached enterprise credentials against single-factor remote administration portals, including Remote Desktop Protocol (RDP) and Secure Shell (SSH) endpoints.
Phishing and Initial Access Brokers: Purchasing active session cookies and corporate access tokens traded on underground markets.
Organizations can proactively assess perimeter exposure and vulnerable services by utilizing Attack Surface Management to discover and eliminate unauthenticated external access points.
2. Discovery, Defense Evasion, and Privilege Escalation
Once initial execution is achieved, Panzer operators conduct internal discovery (T1046) using built-in command-line tools and native administrative utilities. Operators focus on harvesting domain credentials through LSASS memory dumping (T1003) and token manipulation. To prevent real-time intervention, the malware attempts defense impairment (T1562.001) by terminating security services, halting Endpoint Detection and Response (EDR) processes, and clearing Windows event logs.
To guarantee maximum operational disruption, the payload systematically disables local backup mechanisms and recovery points (T1490). On Windows hosts, the ransomware issues commands via vssadmin.exe, wbadmin.exe, and WMI queries to purge shadow copies:
vssadmin.exe delete shadows /all /quiet
wbadmin delete catalog -quiet
wmic shadowcopy delete
3. Hypervisor Exploitation and VMware ESXi Targeting
Panzer includes a dedicated command-line encryptor designed specifically for Linux and VMware ESXi systems. When executed with administrative permissions on an ESXi host, the payload enumerates active virtual machines using native virtualization management utilities. The malware terminates active guest instances to release file locks on virtual machine disks:
esxcli vm process list
vim-cmd vmsvc/getallvms
vim-cmd vmsvc/power.off <vmid>
Following process termination, the binary encrypts .vmdk, .vmx, and .vmsn files using robust cryptographic algorithms, effectively disabling all guest operating systems operating under the hypervisor simultaneously.
4. Staging and Data Exfiltration
Prior to deploying the encryption routine across local storage and shared volumes, Panzer affiliates stage targeted databases, document repositories, and confidential archives. Staged archives are exfiltrated over encrypted channels (T1048) using cloud storage utilities such as Rclone or secure FTP tunnels to adversary-controlled command and control infrastructure.
Adversary Profile: Panzer Ransomware
- Origin
- Ransomware-as-a-Service (Surfaced Aug 2026)
- Motivation
- Financial Extortion
- Targets
- Healthcare and supported living providers (SMCare)Multi-platform enterprise infrastructureVMware ESXi virtualization clusters
- TTPs
- Double-extortion model with automated Tor countdownsCross-platform payloads (Windows, Linux, FreeBSD, ESXi)vssadmin/wbadmin shadow copy and backup catalog purgeAffiliate vetting via Tox messaging with 80/20 split
Who Is Behind the Panzer Ransomware Operation
Panzer functions as a Ransomware-as-a-Service (RaaS) enterprise that surfaced in August 2026. The core operators maintain the foundational codebase, infrastructure, and Tor negotiation portals, while delegating network intrusion and payload execution to screened criminal affiliates under an approximate 80/20 revenue distribution model.
Prospective affiliates are vetted through encrypted messaging protocols, including Tox communications, before gaining access to customized build dashboards. The group adopts an aggressive double-extortion posture, combining irreversible file and hypervisor encryption with the systematic exfiltration and publication of enterprise records on public dark web forums.
Enterprises looking to assess exposure from leak sites or identify compromised internal accounts circulating on cybercriminal channels can evaluate their domain footprint through a dedicated assessment with Dark Web Monitoring.
Free exposure check
Dark Web Scanner
check dark web mentions, compromised account indicators, malware log signals, public breach exposure, and recent underground market activity for your domain.
SMCare Incident Blast Radius
- VMware ESXi Hypervisors & VMDKshigh
- 33 GB Stolen Confidential Recordshigh
- UK GDPR Compliance Obligationshigh
- 20-21 Day Extortion Pressure Timermedium
Enterprise Impact and Extortion Pressure
The Panzer double-extortion framework imposes multi-tiered operational, legal, and financial pressures on target organizations. In healthcare, supported living, and public services, downtime directly impacts care delivery and sensitive patient record confidentiality.
Operational Disruption: Mass hypervisor encryption halts core applications, electronic records management, and communication systems.
Regulatory Exposure: The exfiltration of confidential customer, patient, and employee data triggers mandatory reporting requirements under data protection regulations such as the UK GDPR and Data Protection Act 2018.
Reputational Damage and Extortion Timers: The publication of corporate identities on dedicated leak sites creates public visibility, while active countdown timers place psychological pressure on executive leadership.
Detection, Containment, and Incident Response Strategies
Defending against aggressive RaaS operations like Panzer requires layered controls, robust detection telemetry, and continuous security validation. Security teams should implement the following technical defense measures:
Immediate Threat Hunting and Detection Logic
Audit Hypervisor Access: Continuously monitor ESXi management interfaces for unauthorized SSH logins, abnormal shell invocations, and script-driven execution of
vim-cmdoresxcliutilities.Detect Shadow Copy Deletion: Deploy behavioral endpoint monitoring rules alerting on command-line attempts to execute
vssadmin.exe,wmic shadowcopy, or catalog deletions.Flag Credential Access: Monitor access handles opened against the
lsass.exeprocess and inspect endpoints for unauthorized execution of credential extraction tools.Monitor Outbound Data Volumes: Set automated alerts on abnormal egress network traffic, particularly large file transfers directed toward public cloud object storage or unfamiliar external IP addresses.
Containment and Hardening Recommendations
Segment Management Interfaces: Isolate ESXi, vCenter, backup infrastructure, and network appliance management planes onto dedicated VLANs accessible only via multi-factor authenticated jump hosts. Disable SSH across hypervisors when not actively required.
Maintain Immutable, Air-Gapped Backups: Ensure all system backups are stored in an immutable, offline, or cloud-isolated state to prevent malicious encryption or deletion during an intrusion.
Enforce Phishing-Resistant MFA: Mandate robust multi-factor authentication across all external access portals, VPN concentrators, and enterprise cloud accounts to mitigate credential reuse attacks.
Validate Defenses with Proactive Testing: Perform structured offensive simulations and technical evaluations using Penetration Testing to identify misconfigurations and lateral movement vectors before malicious actors exploit them.
How to Defend Against Similar Threats
- Isolate and restrict VMware ESXi and vCenter management interfaces to dedicated VLANs with multi-factor authenticated jump boxes.
- Verify the operational integrity and immutability of offline backups to ensure recovery without reliance on decryption tools.
- Monitor endpoint process telemetry for unauthorized shadow copy deletion commands and credential dumping against LSASS.
- Enforce phishing-resistant multi-factor authentication across all remote access gateways and administrative accounts.
Threat Intel FAQ
What is Panzer ransomware?
What data did Panzer claim to exfiltrate in the SMCare breach?
How does Panzer target virtualization environments like VMware ESXi?
Could a similar threat affect your organization?
If your team may be exposed to a similar threat, FemtoSec can help validate blast radius, prioritize remediation, and connect the issue to a practical security program.
Related Threats
October 16, 2026
Play Ransomware Targets The Innovation Group
Play ransomware operators have targeted United States management consulting firm The Innovation Group, publishing claims on their dark web leak site with a four to five day deadline to release stolen corporate data.
September 9, 2026
Vexy Ransomware Targets Retailer in 24GB Data Leak
The Vexy ransomware group has published an extortion listing targeting Argentinian retailer Librería Santa Fe, claiming 24.2 GB of exfiltrated data with a 20-day publication ultimatum. Explore technical analysis, attack chains, and defensive containment strategies.
October 5, 2026
Spirals Ransomware Hits Seven Seas Group in GCC
Spirals ransomware has claimed the compromise of GCC-based maritime services provider Seven Seas Group, demanding ransom under a strict data leak countdown. This incident underscores critical risks across regional logistics and transportation infrastructure.