NSPA Targeted by Akira Ransomware Attack
National Standard Parts Associates, Inc has fallen victim to an Akira ransomware attack, with 53 GB of sensitive data exfiltrated, including employee personal documents.
Key Takeaways
- 53 GB of organizational data was exfiltrated by the Akira ransomware group.
- The compromised data includes sensitive PII such as passports, SSNs, and drivers licenses.
- The incident highlights the critical vulnerability of manufacturing firms to double-extortion tactics.
- Proactive defense through offensive security is essential for mitigating modern ransomware risks.
Overview of the NSPA Ransomware Incident
The manufacturing sector continues to face significant challenges as National Standard Parts Associates, Inc (NSPA) has become the latest victim of an Akira ransomware attack. Reports indicate that threat actors successfully exfiltrated approximately 53 GB of organizational data. The breach includes highly sensitive information, such as employee personal documents including passports, drivers licenses, and social security numbers, alongside contracts, agreements, internal financial data, and various non-disclosure agreements.
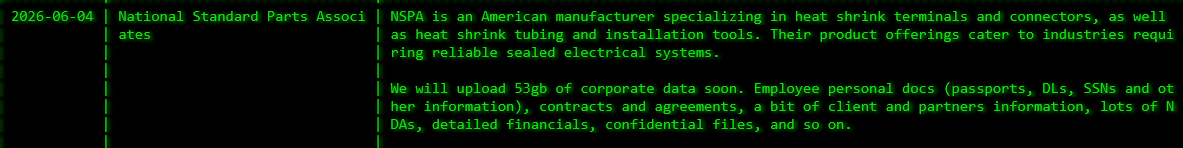
This incident underscores the persistent threat posed by ransomware groups targeting mid-to-large enterprises. For manufacturing firms, the combination of operational technology and sensitive corporate data creates a lucrative target for double-extortion tactics, where attackers steal data before encrypting local systems to force a payout.
Why Manufacturing Remains a Primary Target
Manufacturing organizations are often perceived as having large, complex attack surfaces that may lack the rigorous security controls found in other high-compliance sectors. Attackers look for initial access vectors such as unpatched vulnerabilities, weak remote access controls, or compromised credentials. Once inside, they move laterally to locate intellectual property, financial records, and PII that can be used for secondary extortion or sold on dark web marketplaces. For a comprehensive look at how to secure your digital presence, explore our Attack Surface Management services.
The Anatomy of an Akira Attack
Akira ransomware is known for its sophisticated tactics, often prioritizing long-term persistence in the network to identify high-value data. The breach of NSPA highlights the critical need for proactive defenses. Simply having a firewall is insufficient. Enterprises must assume breach and implement continuous monitoring and offensive validation to identify gaps before adversaries can exploit them. We recommend conducting regular Penetration Testing to identify weak points in your infrastructure and applications.
The inclusion of employee personal data significantly increases the severity of this incident, as it carries heavy regulatory and legal implications. Enterprises must go beyond perimeter security and ensure that data at rest is protected and that access logs are monitored for anomalous behavior indicative of exfiltration.
Strategic Resilience for GCC Enterprises
In the GCC region, manufacturing firms and industrial partners must prioritize resilience against such incidents. The threat landscape is evolving, and traditional compliance measures often fall short of addressing the specific techniques used by groups like Akira. FemtoSec provides enterprise-grade cybersecurity through a proactive operating model, ensuring your defenses are aligned with both current global threats and regulatory frameworks. We help businesses harden their infrastructure through offensive security and compliance-first strategies.
Effective risk mitigation requires a multi-layered approach that includes regular vulnerability assessments, robust identity management, and employee awareness training. Relying on legacy systems without modern, AI-powered security oversight is an open invitation for sophisticated threat actors to gain a foothold in your network.
How to Defend Against Similar Threats
- Conduct an immediate audit of all remote access points and credentials.
- Implement comprehensive monitoring to detect unauthorized data exfiltration.
- Schedule a professional penetration test to uncover vulnerabilities before attackers find them.
- Review internal data access policies to ensure the principle of least privilege is strictly enforced.
Threat Intel FAQ
What is the primary risk of an Akira ransomware attack?
How can manufacturing firms prevent similar breaches?
Could a similar threat affect your organization?
If your team may be exposed to a similar threat, FemtoSec can help validate blast radius, prioritize remediation, and connect the issue to a practical security program.
Related Threats
October 23, 2026
Kazu Ransomware Targets Insurance Sector in 366 GB Breach
Kazu ransomware operators have listed South African insurer Rand Mutual Assurance on their dark web leak portal, claiming 366 GB of exfiltrated corporate records. This intelligence brief examines Kazu's attack tradecraft, LockBit lineage, operational impact, and concrete detection rules.
October 16, 2026
Play Ransomware Targets The Innovation Group
Play ransomware operators have targeted United States management consulting firm The Innovation Group, publishing claims on their dark web leak site with a four to five day deadline to release stolen corporate data.
October 5, 2026
Spirals Ransomware Hits Seven Seas Group in GCC
Spirals ransomware has claimed the compromise of GCC-based maritime services provider Seven Seas Group, demanding ransom under a strict data leak countdown. This incident underscores critical risks across regional logistics and transportation infrastructure.